Security
Hardening architecture: the technical “recipe” for an impregnable infrastructure
Is your server secure? Discover Oksigenia's technical recipe: 5 critical steps, from Docker to the 3-2-1 rule, to harden your infrastructure today.
Published updated 3 min read
In IT security there is a maxim: obscurity is not protection. Believing that nobody will attack you because your company is small is like leaving your office door open on the assumption that thieves only go after banks. Today's attacks are automated; they are bots hunting for badly locked doors through mass IP scans.
Today we are opening the Oksigenia cookbook. We will not give you a tutorial, but rather the architectural “ingredients” needed to turn a vulnerable environment into a digital fortress.
“There are only two types of companies: those that have been hacked and those that don't yet know they have been.” — James Comey, former Director of the FBI.
The 70 million failure (Target, 2013)
One of the most studied cases in cybersecurity did not happen because of a fault in the main servers, but because of poor privilege management. In 2013, the retail chain Target suffered the theft of data belonging to 70 million customers.
The origin? The attackers stole the credentials of an external air-conditioning (HVAC) contractor that had access to the billing system. There was no isolation. The system trusted that any validated user could move freely across the entire network. This landmark event cemented what we now know as the need for “layer isolation”.
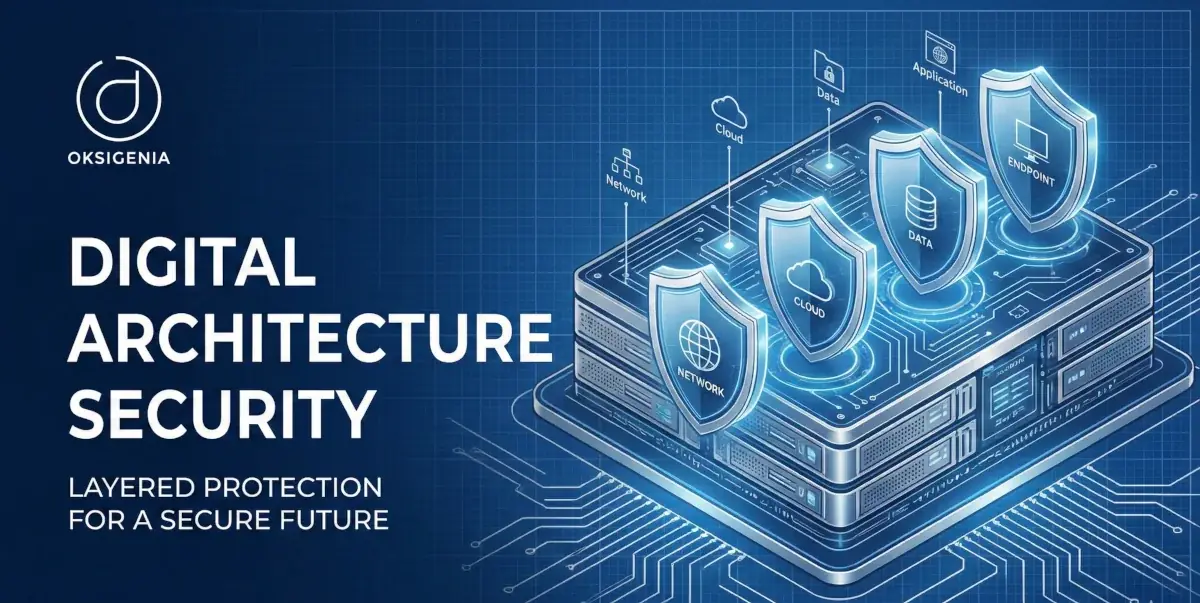
The Oksigenia recipe: 5 layers of hardening
1. The principle of “least privilege”
Inspired by cases such as Target's, the rule is simple: nobody should have more access than is strictly necessary. Using the root or administrator account for everyday tasks is a critical architectural error.
// Default access logic at Oksigenia:
if (user.action == "maintenance") {
    access = "temporary_restricted";
} else {
    access = "denied_by_default";
}
// Trust is a security flaw.
2. Port obfuscation (security by design)
Port 22 (SSH) is the number one target of scans worldwide. Moving the “front door” to non-standard ports above 10,000 does not eliminate the risk, but it clears 99% of the noise and automated attacks from the logs. If they cannot see you, they cannot hit you.
3. Isolation through containers (Docker)
At Oksigenia we do not install “loose” services. We use Docker so that each application lives in its own sealed cell. If a website suffers a vulnerability, the attacker is trapped inside the container, with no visibility of the database or the rest of the server. It is the equivalent of a ship's watertight compartments.
4. Proactive defence (IPS/IDS)
We implement systems that “learn” from malicious behaviour. If an IP repeatedly tries to log in with the wrong credentials, the system bans it at firewall level before it can do any damage.
# Active threat monitoring:
$ check-threat --status
> Scanning logs...
> 452 brute-force attempts detected from IP 1.2.3.4
> Action: PERMANENT_BAN_TRIGGERED
5. The golden rule of backup: 3-2-1
A system is only secure if it is recoverable. Following industry standards, the recipe is: 3 copies of the data, on 2 different media, with 1 of them outside the main infrastructure (off-site).
The difference between “having a website” and “being protected”
Applying these points requires a level of technical precision that goes well beyond a simple click in a conventional hosting control panel. At Oksigenia, when we set up a VPS, an online shop or a Moodle environment, these 5 steps are not extras; they come as standard.
Our experience in the retail sector has taught us that security is not a luxury, it is the foundation of business continuity. If your foundations are weak, all the marketing in the world will be of no use when the system fails.